October is Cybersecurity Awareness Month, and we’re giving the leaders behind enterprise security the spotlight!
In this special edition of CxOs on the Move, we’re celebrating 70 CISOs and security executives who have taken on new roles this year. These executives are stepping into positions at some of the world’s most recognizable organizations, taking responsibility for protecting critical systems and strengthening cybersecurity programs.
Join us in congratulating them on their new chapters!
Assaf Keren – Chief Information Security Officer at Meta
Meta has appointed Assaf Keren as Chief Information Security Officer, succeeding Guy Rosen following his retirement after 13 years with the company. Keren joins from Qualtrics, where he served as Senior Vice President and Chief Security Officer, after previously spending nine years at PayPal in a series of security leadership roles, including Chief Information Security Officer. He brings extensive experience leading enterprise security programs across global technology companies.
Christopher Davis – Chief Security Officer at IBM
Christopher Davis has stepped into the role of Chief Security Officer at IBM. He brings more than three decades of security leadership experience across government and industry, including senior roles at Microsoft, Walmart, Amgen and NASCAR. Earlier in his career, Davis spent 23 years with the FBI leading investigations and security operations around the world. At IBM, he will help the company and its clients manage cyber threats, geopolitical uncertainty and other evolving risks.
Philip Martin – Chief Information Security Officer at Uber
Uber has appointed Philip Martin as Chief Information Security Officer, bringing in an experienced cybersecurity leader with a background spanning technology, financial services, and the military. Martin joins Uber after more than a decade at Coinbase, where he served as Chief Security Officer since 2016. In that role, he led a global team of more than 250 professionals responsible for cybersecurity, trust and safety, physical security, technology governance, risk and compliance, and business resilience across the company’s consumer and enterprise operations.
Kim Keever – Chief Security Officer at Lumen Technologies
Lumen Technologies has tapped Kim Keever as Chief Security Officer. She will oversee security across the company’s physical, digital and operational assets, including critical infrastructure and network-as-a-service offerings. Keever most recently served as Chief Information Security Officer at Cox Communications, where she spent more than a decade leading cybersecurity risk management. She previously held several security leadership roles at The Coca-Cola Company, including CISO of its Bottling Investments Group.
Daniel Dubowski – Senior Vice President and Chief Information Security Officer at Marriott International
Marriott International has brought on Daniel Dubowski as Senior Vice President and Chief Information Security Officer, where he will help strengthen cybersecurity and resilience across the company’s global enterprise. Dubowski joins from Hertz, where he also served as CISO, and brings experience leading cybersecurity and risk programs across hospitality, travel, financial services, and healthcare. He succeeds Arno Van Der Walt and will report to Global CIO Naveen Manga. At Marriott, Dubowski will focus on protecting guests, associates, owners, and partners as the company continues its multiyear technology transformation and expands its use of AI and automation.
Ann Barron-DiCamillo – Executive Vice President and Global Chief Information Security Officer at U.S. Bank
U.S. Bank has appointed Ann Barron-DiCamillo as Executive Vice President and Global Chief Information Security Officer, placing her in charge of the bank’s global information security strategy and cyber resilience efforts. Barron-DiCamillo joins from Citi, where she most recently served as Managing Director and Global Head of Tech Optimisation. She previously held the role of Managing Director and Global Head of Cyber Operations, leading cybersecurity initiatives across the bank. She brings more than 25 years of experience spanning threat intelligence, cyber operations, risk management, technology transformation and security governance. Prior to Citi, Barron-DiCamillo was Vice President of Cyber Threat Intelligence and Incident Response at American Express.
Randi Kieffer – Chief Information Security Officer at USAA
A few months after appointing Dan Griffiths as Chief Information Officer, USAA has brought on Randi Kieffer as Chief Information Security Officer, following her nine-year tenure at Capital One, where she most recently served as Managing Vice President of Cyber Operations & Intelligence. Kieffer also brings federal cybersecurity experience, including previous roles as CISO at the Transportation Security Administration and Deputy Director of the Department of Homeland Security’s National Cybersecurity & Communications Integration Center.
Christian Winward – Chief Information Security Officer at PNC
PNC has appointed Christian Winward as Chief Information Security Officer, elevating a longtime banking technology executive to lead the company’s Enterprise Information Security organization. Winward joins the role after serving as Chief Information Officer at FirstBank, which became part of PNC earlier this year, where he helped modernize the bank’s technology capabilities and supported its integration into PNC. His career with FirstBank spanned more than 30 years, progressing through leadership roles across technology and project management.
Keith Anderson – Chief Information Security Officer at Travelers
Keith Anderson has joined Travelers as Chief Information Security Officer, where he will lead the company’s enterprise cybersecurity strategy and work across the organization to strengthen its security posture and protect customers and technology assets. Anderson joins from JetBlue, where he most recently served as Vice President of Technology Infrastructure and Chief Information Security Officer. Earlier in his career, he held cybersecurity leadership roles at WarnerMedia and AT&T, bringing more than two decades of experience leading enterprise security and technology organizations.
Ruben D. Chacon – Vice President and Global Chief Information Security Officer at ADM
ADM has added Ruben D. Chacon as Vice President and Global Chief Information Security Officer. He will lead efforts to strengthen cyber resilience and integrate cybersecurity into the company’s technology and business operations. Chacon most recently served as Global Vice President and Chief Information Security Officer at Eaton. He previously held security leadership roles at CDW, Constellation Brands and Mondelēz International.
Chaim Mazal – Chief Information Security Officer at GitLab
GitLab has named Chaim Mazal as its new Chief Information Security Officer, tasking him with leading the company’s global security organization and overseeing the security of both the business and its platform. Mazal joins from Gigamon, where he served as Chief AI and Security Officer, overseeing the company’s security function and AI governance initiatives. He previously held senior security leadership roles at Kandji and ActiveCampaign and brings more than 15 years of cybersecurity experience. At GitLab, he will help shape the company’s approach to AI security as organizations increasingly adopt AI agents and confront emerging AI-driven threats.
John Opala – Chief Information Security Officer at Ralph Lauren
John Opala has joined Ralph Lauren as Chief Information Security Officer, bringing extensive cybersecurity leadership experience across global consumer brands. Most recently, he served as Vice President of IT and Global Chief Information Security Officer at HanesBrands, following an earlier stint as Vice President of IT and Global CISO at McCormick & Company. In his new role, Opala will lead Ralph Lauren’s cybersecurity strategy, helping strengthen security, resilience, and trust across the enterprise.
Tony Arous – Chief Information Security Officer at Toast
Tony Arous has joined Toast as Chief Information Security Officer. Bringing more than 20 years of cybersecurity leadership experience, Arous will lead the company’s security strategy as it expands across international markets, enterprise, and retail. In his new role, he will focus on strengthening Toast’s security posture to support the continued growth of its global technology and payments platform while protecting customers and enabling the business.
John Koester – Senior Vice President and Chief Information Security Officer at Hertz
John Koester has joined Hertz as Senior Vice President and Chief Information Security Officer. Koester joins the company after two years as Vice President and CISO at Graphic Packaging International. Previously, he spent more than eight years at HD Supply, holding several cybersecurity leadership positions, including Vice President and CISO, Senior Director and CISO, and Director of Information Security and CISO. Earlier in his career, he served as Director of Security Operations at Viewpost. At Hertz, Koester will work with the company’s cybersecurity team to strengthen its existing security foundation and guide future initiatives.
David Soto – Chief Information Security Officer at Trellix
Trellix has welcomed David Soto as Chief Information Security Officer, where he will lead the company’s enterprise security program, resilience efforts, and Customer Zero program. Soto brings more than 25 years of cybersecurity leadership experience across regulated industries, most recently serving as Head of Infrastructure Security at Amazon. There, he scaled a security program spanning more than 4,000 sites across 30 countries and helped embed security into global operations infrastructure. At Trellix, Soto will focus on strengthening enterprise security and cyber resilience as organizations contend with machine-speed threats.
Adam Zoller – Chief Information Security Officer at Nike
Nike has tapped Adam Zoller as Chief Information Security Officer following nearly two years in the same role at CrowdStrike. Zoller previously spent more than five years as Senior Vice President and Global CISO at Providence, overseeing cybersecurity for a healthcare system with more than 50 hospitals, 1,000 clinics, and 120,000 caregivers. Earlier in his career, he held several security leadership positions at General Electric, including CISO of GE Healthcare, along with roles at GE Capital Retail Bank/Synchrony Financial and GE Corporate.
Justin Henkel – Chief Information Security Officer at SolarWinds
SolarWinds has appointed Justin Henkel as Chief Information Security Officer, adding a seasoned cybersecurity leader with experience spanning military intelligence, threat intelligence, and enterprise security operations. Henkel joins the company from OneTrust, where he spent nearly five years and most recently served as Deputy CISO. During his time there, he helped build programs focused on enterprise risk, resilience, and security operations after initially joining as Head of the CISO Center of Excellence. At SolarWinds, Henkel will oversee the company’s information security strategy and help advance its security posture as it continues expanding its observability and IT management offerings.
Tera Ladner – Senior Vice President and Global Chief Information Security Officer at Aflac
Aflac has elevated Tera Ladner to Senior Vice President and Global Chief Information Security Officer after she most recently served as Deputy Global CISO. During more than a decade with Aflac, Ladner has taken on increasingly senior responsibilities across information risk management, governance, and global security. As Global CISO, she now oversees Aflac’s enterprise information security strategy across its global operations.
Manju Mudé – Chief Information Security Officer at U.S. Department of the Treasury
Manju Mudé has taken on the role of Chief Information Security Officer at the U.S. Department of the Treasury, bringing more than 25 years of cybersecurity leadership experience across the public and private sectors. She joins Treasury after serving as Global CISO at Oportun and previously held senior security leadership roles at Splunk, Yahoo, Apple, and Bank of America. Throughout her career, Mudé has led cyber risk, regulatory compliance, incident response, and security transformation initiatives, with extensive experience helping organizations strengthen resilience and navigate growth.
Mike Marshall – Chief Information Security Officer at the State of California
California has tapped Mike Marshall as Chief Information Security Officer, bringing 18 years of public-sector cybersecurity experience to the role. Marshall most recently served as Acting Information Officer at the California Environmental Protection Agency, where he previously spent five years as Information Security Officer. He began his public-sector cybersecurity career at the California Public Employees’ Retirement System and has worked with the California Department of Technology on statewide security initiatives. As CISO, Marshall will help lead implementation of Cal-Secure 2.0, California’s cybersecurity roadmap focused on workforce development, government coordination, information sharing, and security technology modernization.
Jordan Avnaim – Global Chief Information Security Officer at Allied Universal
Allied Universal has named Jordan Avnaim Global Chief Information Security Officer, where he will lead the company’s global cybersecurity strategy and operations across more than 100 countries and territories. Avnaim brings more than 20 years of experience in cybersecurity, technology risk, and regulatory compliance, previously serving as CISO at Hyundai AutoEver America and Entrust, along with senior security leadership roles at Capital Group Companies. At Allied Universal, he will oversee cybersecurity teams and resources while developing a risk-based security program focused on protecting employees, systems, data, and technology platforms and strengthening cyber resilience across the organization.
John Fung – Deputy Chief Information Security Officer and Director of Cyber Defense at Rockwell Automation
Rockwell Automation has promoted John Fung to Deputy Chief Information Security Officer and Director of Cyber Defense. He will lead cyber defense operations across security operations, incident response, threat intelligence, vulnerability management, digital forensics and insider risk. Fung has spent more than four years with Rockwell Automation, most recently serving as Director of Security Operations and Cyber Defense. He previously held cybersecurity leadership roles at MorganFranklin Consulting, Cimpress and Raytheon Technologies.
Dan Holland – Vice President and Chief Information Security Officer at Tampa General Hospital
Tampa General Hospital has promoted Dan Holland to Vice President and Chief Information Security Officer after he spent the past two years as Deputy CISO. In his new role, Holland will lead the health system’s cybersecurity program, building on the security strategy established during his predecessor’s tenure. He brings extensive cybersecurity leadership experience and has played a key role in protecting the organization’s patients, operations, and technology environment.
Srini Uppugonduri – Senior Vice President and Chief Information Security Officer at Novant Health
Srini Uppugonduri has been promoted to Senior Vice President and Chief Information Security Officer at Novant Health, where he will lead the organization’s cybersecurity strategy, governance, cyber operations, risk management, and resilience initiatives. Previously serving as Vice President of Information Security, Uppugonduri played a key role in strengthening the health system’s enterprise security posture, supporting strategic integrations, advancing AI-driven operations, and overseeing cybersecurity governance. He brings more than 20 years of experience in enterprise cybersecurity, infrastructure, and technology operations.
Mangoné Fall – Chief Information Security Officer at Guthrie Clinic
Guthrie Clinic has named Mangoné Fall Chief Information Security Officer, placing him in charge of the health system’s enterprise information security strategy, including cyber risk management, data protection, and initiatives designed to safeguard patient and caregiver information. Fall brings more than 25 years of technology and cybersecurity leadership experience and most recently served as Chief Information Security Officer at Duke Health. Prior to that, he held senior cybersecurity leadership roles at Cleveland Clinic, including Deputy CISO and Executive Director of Cybersecurity.
Henrik Smith – Chief Information Security Officer at Infoblox
Henrik Smith has been appointed Chief Information Security Officer at Infoblox, where he will lead the company’s global security strategy, cyber resilience, and risk management efforts. He joins from Amazon, where he served as Head of Security for Devices and Services, and previously held senior security leadership roles at Salesforce and Amazon Web Services, bringing nearly 30 years of experience in cloud security, enterprise security, and risk management.
Mark Carter – Chief Information Security Officer at Socure
Mark Carter has been appointed Chief Information Security Officer at Socure, where he will lead the company’s enterprise security, cyber risk, governance, compliance, resilience, and IT strategy. Carter brings more than 25 years of leadership experience in cybersecurity and technology, joining from Navan, where he served as CISO. He previously held CISO roles at Tesla and Vimeo, and senior leadership positions at Salesforce, Amazon, Google, Microsoft, PayPal, VMware, and Gemalto.
Paul Black – Chief Information Security Officer at Tanium
Paul Black has joined Tanium as Chief Information Security Officer, taking responsibility for the company’s global security program as it expands the use of AI across its operations and advances its customer-zero strategy. Black most recently served as CISO at Turing, where he led security efforts in an AI-focused environment. His background also includes senior security and technology leadership roles at Upwork, McKesson, PayPal, and J.P. Morgan.
Grant Yacomeni – Chief Information Security Officer at Gigamon
Gigamon has appointed Grant Yacomeni as Chief Information Security Officer, overseeing information and product security, cybersecurity and IT operations, and governance, risk, and compliance. Yacomeni brings more than a decade of cybersecurity and national security experience, most recently holding leadership roles within the U.S. Intelligence Community, including the Department of Defense, where he led enterprise security programs and 24/7 defensive cyber operations. He previously served in intelligence and cybersecurity roles with the Maryland Army National Guard and is a U.S. Marine Corps veteran.
Erika Dean – Chief Information Security Officer at Tricentis
Tricentis has appointed Erika Dean as Chief Information Security Officer, placing her in charge of the company’s global enterprise cybersecurity, compliance, and product security programs. Dean brings more than 20 years of cybersecurity leadership experience across financial services and technology, including security leadership roles at Robinhood and Capital One. At Tricentis, she will focus on strengthening enterprise and product security, software supply chain protections, AI governance, and cyber resilience as the company expands its Agentic Quality Engineering Platform and customers increase their use of AI.
Patrick McKinney – Chief Information Security Officer at Turing
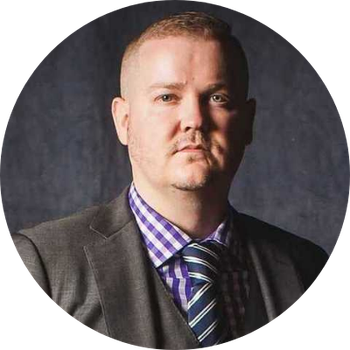
Patrick McKinney has joined Turing as Chief Information Security Officer, taking responsibility for security across the company’s frontier AI and enterprise AI businesses. He most recently served as Vice President of Security and IT at Invisible Technologies, where he was the company’s first dedicated security hire and built its security organization. McKinney previously held security and compliance roles at Dropbox and Coinbase, contributing to the teams that guided each company through its public offering.
Gwen Gann – Chief Information Security Officer at Washington State
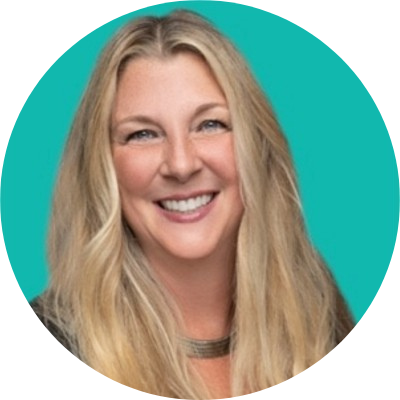
Gwen Gann has been named Washington State’s Chief Information Security Officer. She will lead the Office of Cybersecurity within Washington Technology Solutions (WaTech), overseeing statewide cybersecurity strategy and working with government agencies and security partners. Gann brings more than 30 years of technology leadership experience and most recently served as Technology Director at HealthFirst. She previously spent more than six years as Chief Information Officer at Public Partnerships LLC.
Jason Cradit – Chief Technology Officer and Chief Information Security Officer at EverLine
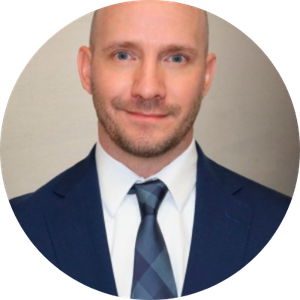
Jason Cradit has been appointed Chief Technology Officer and Chief Information Security Officer at EverLine, where he will lead the company’s technology strategy, cybersecurity, and operational resilience initiatives. Cradit brings more than 25 years of experience securing critical infrastructure across the energy, pipeline, aerospace, and defense sectors. Prior to joining EverLine, he co-founded energy software company Pivvot and held senior cybersecurity, compliance, and operational technology leadership roles supporting infrastructure operators across North America.
David Raymond – Associate Vice President and Chief Information Security Officer at Virginia Tech
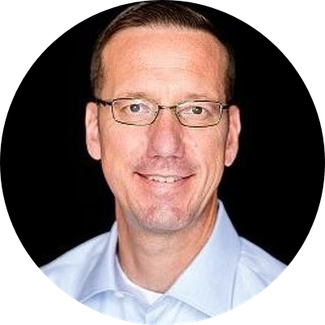
Virginia Tech has named David Raymond Associate Vice President and Chief Information Security Officer, formalizing his leadership of the university’s cybersecurity strategy following the retirement of longtime security leader Randy Marchany. In the role, Raymond will oversee the university’s information security program and serve as the institution’s lead for security-related compliance and reporting. Raymond has spent more than a decade at Virginia Tech, most recently serving in a series of senior leadership roles, including interim vice president for information technology and CIO, interim associate vice president for research computing, and founding director of both the Virginia Cyber Range and U.S. Cyber Range. Before joining the university, he served on the faculty at the United States Military Academy at West Point and retired from the U.S. Army after 26 years of active duty service.
Adam Dimopoulos – Chief Information Security Officer at Entrust
Adam Dimopoulos has been appointed Chief Information Security Officer at Entrust, where he will lead efforts to strengthen the company’s security posture, resilience, and customer trust while supporting secure innovation and business growth. Dimopoulos brings more than 20 years of experience in information security, identity, and risk management, most recently serving as Vice President of Information Security at Synchrony, where he led enterprise-wide identity security and Zero Trust transformation initiatives.
Thomas Hill – Chief Information Security Officer at Candescent
Thomas Hill has been appointed Chief Information Security Officer at Candescent, bringing more than 25 years of cybersecurity leadership experience in digital banking and regulated financial services. He joins from nCino, where he served as CISO, leading enterprise security programs supporting more than 1,850 financial institutions worldwide. Previously, Hill was CIO and CISO at Live Oak Bank, where he helped drive the bank’s cloud-first security strategy.
Ravi Thatavarthy – Chief Information Security Officer at Primo Brands
Ravi Thatavarthy has joined Primo Brands as Chief Information Security Officer. Bringing more than 25 years of cybersecurity leadership experience, Thatavarthy will lead the company’s information security strategy as it supports the growth of its North American beverage business. Prior to joining Primo Brands, he served as Chief Information Officer at EmpiRx Health and has extensive expertise in security strategy, risk management, privacy, compliance, and AI-enabled cybersecurity.
Jonathan Krotz – Chief Information Security Officer at Davis Polk & Wardwell LLP
Jonathan Krotz has joined Davis Polk & Wardwell as Chief Information Security Officer, following more than seven years at PJT Partners. Most recently, he served as Senior Vice President and Head of Information Security and Technology Risk, where he built and led the firm’s cybersecurity and technology risk program. Earlier in his career, Krotz advised the Navy Program Executive Office on cybersecurity and managed security solutions for sensitive government systems. His background also includes engineering roles at Curtiss-Wright Defense Solutions and Vista Research, with experience spanning secure computing and cybersecurity policy for military applications.
Greg Nicoson – Chief Information Security Officer at the U.S. Department of the Treasury’s Departmental Offices
Greg Nicoson has stepped into the Chief Information Security Officer role for the U.S. Department of the Treasury’s Departmental Offices after serving as Data Center Operations Manager. He previously held technology and operations leadership roles at the Inter-American Defense College and the George C. Marshall Center, where he served as Deputy Chief Information Officer. Nicoson also spent nearly 11 years supporting the U.S. Army’s Joint Communications Unit.
Hemant Baidwan – Executive Chief Information Security Officer at Knox Systems
Knox Systems has named Hemant Baidwan as Executive Chief Information Security Officer, where he will lead the company’s cybersecurity program and strengthen security across its AI-driven cloud platform while advancing automated compliance and secure federal cloud adoption. He joins from the U.S. Department of Homeland Security, where he served as Chief Information Security Officer and led enterprise-wide cybersecurity strategy, including Zero Trust initiatives and modernization efforts across mission-critical systems.
Roger Hale – Chief Information Security Officer at 1Kosmos
Roger Hale has joined 1Kosmos as Chief Information Security Officer, where he will lead the company’s internal security, compliance, customer trust, privacy, AI governance, and risk management programs as it expands adoption of its identity verification and passwordless authentication platform. Hale brings more than 20 years of executive cybersecurity leadership experience, joining from Informatica, where he served as Vice President and Chief Information Security Officer and led the company’s security transformation during its transition to a cloud-first data management business. He has also held senior security leadership roles at Agora, BigID, and Veritas/Symantec, and served as CISO-in-Residence and Venture Advisor at YL Ventures, advising early-stage cybersecurity companies on product strategy, security, and go-to-market readiness.
John Podboy – Chief Information Security Officer at Semperis
Semperis has appointed John Podboy as Chief Information Security Officer, where he will lead the company’s security strategy with a focus on risk management, resilience, compliance, and AI-driven cyber defense as the company continues to scale. Podboy brings more than 15 years of cybersecurity and technology leadership experience, including senior roles at Fifth Third Bank, First Citizens Bank, Thomson Reuters, and GE Digital, where he led enterprise security and resilience programs across regulated and global environments.
Kelly Sunderland – Chief Information Security Officer at Platform One
Kelly Sunderland has joined the Department of the Air Force as Chief Information Security Officer for Platform One. He previously supported Platform One through Applied Research Solutions, serving as Deputy Chief Information Security Officer and providing advisory services for more than three years. Sunderland earlier spent nearly 16 years as a Telecommunications Network Engineer with the U.S. Army.
James Wilkinson – Chief Information Security Officer at the City of Dallas
James Wilkinson has been appointed Chief Information Security Officer (CISO) for the City of Dallas, where he will lead the city’s enterprise information security program and help strengthen cyber resilience across critical systems, public services, and city departments. He brings more than 25 years of experience leading cybersecurity and technology initiatives across the military, financial services, aerospace, defense, and the public sector.
Christopher Freytes – Chief Information Security Officer at Alpha Compute
Alpha Compute has appointed Christopher Freytes as Chief Information Security Officer, where he will oversee the company’s global security strategy and help protect its AI infrastructure and confidential computing environments. Freytes brings experience in cloud-native security, zero-trust architecture, and cybersecurity for highly regulated environments. He also serves as a Warrant Officer in Cyber Defense Operations for the U.S. Air National Guard, supporting enterprise and tactical communications systems for national security missions. At Alpha Compute, Freytes will focus on safeguarding enterprise and government workloads, strengthening data protection, and securing the company’s expanding data center infrastructure.
Jeremy Powell – Chief Information Security Officer at Sumo Logic
Jeremy Powell has joined Sumo Logic as Chief Information Security Officer, where he will lead the company’s enterprise cybersecurity strategy, security programs, and product security initiatives as it expands its AI-focused security platform. Powell most recently served as CTO at Lockthreat and brings more than 25 years of experience in cybersecurity leadership, including CISO and CTO roles at Zyston, Verint, and AdTech Global.
Edwin Ng – Chief Information Security Officer at LogicGate
LogicGate has appointed Edwin Ng as Chief Information Security Officer, putting the former Hyatt Hotels executive in charge of the company’s global digital resilience strategy and enterprise security operations. Ng most recently served as Vice President and CISO at Hyatt Hotels Corporation, where he oversaw global security strategy, threat intelligence, vulnerability management, and IT governance, following earlier security leadership roles at United Airlines and McDonald’s.
Patti Degnan – Chief Information Security Officer at Glow
Glow has recruited Patti Degnan as Chief Information Security Officer, where she will build and lead the company’s security, IT, compliance, privacy, and customer trust organizations. Degnan brings nearly two decades of cybersecurity and privacy experience, most recently serving as an Operating Partner at Andreessen Horowitz, where she advised companies on securing AI-native technologies. She previously served as CISO at Notion, where she founded the security organization and scaled it as the company grew past 100 million users. Earlier in her career, Degnan held leadership roles at Looker and Informatica. At Glow, she will also work with product and engineering teams to strengthen security across the company’s enterprise endpoint security offerings.
Todd Dekkinga – Chief Information Security Officer at Sycomp
Todd Dekkinga has joined Sycomp as Chief Information Security Officer, where he will lead the company’s expanding security practice and oversee its cybersecurity strategy, governance, risk management, compliance, and security operations. Dekkinga brings more than 25 years of cybersecurity and IT leadership experience, having held executive and advisory roles across the technology, financial services, and life sciences sectors. He also serves in leadership positions within several CIO and CISO organizations, including the Bay Area Biotech CIO Group, CISE, SIM SF Bay Area, and The CISO Society.
Rob Yox – Chief Information Security Officer at Lightedge
Lightedge has welcomed Rob Yox as Chief Information Security Officer, where he will lead the company’s security and compliance organizations as it continues expanding its cloud and hybrid infrastructure services. Yox brings more than 25 years of experience in cybersecurity, enterprise technology, and risk management, with a background building security programs for regulated cloud and SaaS environments. In his new role, he will help strengthen Lightedge’s security strategy while advancing customer trust and compliance initiatives.
Alexander Truskovsky – Chief Information Security Officer at EigenQ
EigenQ has promoted Alexander Truskovsky to the newly created role of Chief Information Security Officer, expanding his responsibilities after serving as Vice President of Cryptography. In the role, he will lead the company’s cybersecurity strategy while helping embed security across its products and operations as it advances quantum technologies. A cryptography expert and enterprise solutions architect, Truskovsky has played a key role in shaping EigenQ’s technology, security architecture, and product strategy.
Stephen Garcia – Chief Information Security Officer at BreachRx
BreachRx has appointed Stephen Garcia as Chief Information Security Officer, placing him in charge of the company’s internal security program. Garcia will also bring a working CISO perspective to the development of BreachRx’s cyber incident response platform as organizations contend with faster and more coordinated AI-driven threats. He brings more than two decades of experience building security programs across financial services, technology, gaming, and other regulated industries. His previous leadership experience includes roles at Western Union, BNP Paribas, Broadridge Financial, Johnson Controls, ConsenSys, FanDuel, and Napster.
Israel Barak – Chief Information Security Officer at 7AI
7AI has named Israel Barak as Chief Information Security Officer, where he will lead the company’s security organization and help scale its AI-driven model for security operations as enterprises adopt agentic approaches. In the role, he will focus on building the team and capabilities that support customers transitioning to AI-driven investigations and workflows. Barak joins from Cybereason, where he served as CISO leading global security strategy, and brings more than two decades of experience across security operations, threat intelligence, and incident response.
Paras Malhotra – Chief Information Security Officer at Starburst

Paras Malhotra has been named Chief Information Security Officer at Starburst, where he will lead information security, governance, risk and compliance, and product security across the company’s SaaS and on-premises offerings. He joins from Datadog, where he served as Senior Director of Information Security and led customer trust, risk management, security monitoring, and AI governance programs.
Amy Brown-Slawson – Chief Information Security Officer at Advanced IT
Advanced IT has welcomed Amy Brown-Slawson as Chief Information Security Officer, where she will lead the company’s enterprise cybersecurity strategy, information security governance, risk management, regulatory compliance, and security operations. Brown-Slawson brings nearly 20 years of IT and cybersecurity leadership experience, most recently serving as Chief Information Security Officer and IT Security Manager at Aurora Flight Sciences. She previously spent more than 14 years as Director of IT and Security at Orbit Logic. At Advanced IT, Brown-Slawson will focus on strengthening cyber resilience, protecting critical systems and information, and advancing security and compliance capabilities supporting the company’s federal and defense work.
Max Mansur – Chief Information Security Officer at USAC
USAC has promoted Max Mansur to Chief Information Security Officer after he served as Acting CISO since April. Mansur has spent nearly a decade with the organization, previously serving as Deputy CISO and IT Security Compliance Senior Manager, with responsibilities spanning security governance, risk management, identity and access management, supply chain risk, and vulnerability monitoring. Before USAC, he served as a Program Manager at Appian and spent more than 12 years at SWIFT in product, technical, and project management roles.
Chad Holmes – Chief Information Security Officer at Texas Attorney General’s Office
Chad Holmes has been named Chief Information Security Officer for the Texas Office of the Attorney General, marking his first public-sector role after more than 25 years in private-sector cybersecurity leadership. Holmes brings extensive experience in incident response, threat intelligence, artificial intelligence, and cyber resilience. As CISO, he will oversee the agency’s cybersecurity strategy, AI-enabled operations, breach response, and public-private collaboration to strengthen the office’s security posture.
Donna Tatro – Chief Information Security Officer at Princeton University
Princeton University has named Donna Tatro Chief Information Security Officer, formalizing her leadership of the institution’s information security program after serving in the role on an interim basis since March 2025. She oversees efforts to protect the University’s data, systems, and digital identities while advancing cybersecurity awareness and resilience across campus. Tatro has been with Princeton since 1995, most recently guiding initiatives that strengthened risk management practices, incident response capabilities, and community-wide security education.
Pamela McLeod – Chief Information Security Officer at the State of New Hampshire
New Hampshire has named Pamela McLeod as its new Chief Information Security Officer, bringing a longtime education sector cybersecurity leader into state government. The appointment was confirmed by State Chief Information Officer Denis Goulet. McLeod joins from ACT, where she served as Cyber Director. She has more than 15 years of experience focused on cybersecurity in education, including serving as Chief Information Security Officer for the Concord School District in New Hampshire. Her background includes work with school systems and local governments that face frequent ransomware and cyberattack activity.
Bertrum Carroll – Chief Information Security Officer at the State of Nevada
Nevada has selected Bertrum Carroll as Chief Information Security Officer, placing him within the Office of Information Security and Cyber Defense to lead risk management, incident response coordination, and security governance across the state’s executive branch. Carroll joins from the private sector, where he held security leadership roles at companies including Employers, SC Johnson, and Johnson Controls, bringing more than two decades of information security experience.
Scott Scheidt – Chief Information Officer and Chief Information Security Officer at Accelecom
Accelecom has recruited Dr. Scott Scheidt as Chief Information Officer and Chief Information Security Officer, a newly combined role overseeing information technology, operational and business support systems, enterprise security, and emerging AI capabilities. Scheidt joins from a regional cybersecurity and managed services provider, where he served as Chief Security Officer and built a virtual CISO practice supporting clients across the U.S., Canada, and Australia. He also brings more than three decades of U.S. Army Reserve experience in intelligence and cyber operations. At Accelecom, Scheidt will lead its OSS/BSS and internal IT environments, enterprise security program, market-facing security offerings, and adoption of AI-driven automation.
Jeffrey Javits – Senior Vice President and Chief Information Security Officer at West Coast Community Bank
West Coast Community Bank has added Jeffrey Javits as Senior Vice President and Chief Information Security Officer, placing him in charge of the bank’s information security programs, regulatory compliance, and cyber risk management. He brings experience from a recent role as a virtual CISO for a San Francisco-based software startup, following earlier leadership positions including Chief Information Officer and Corporate Security Officer at Heritage Bank of Commerce.
John Visneski – Chief Information Security Officer at Green Impact Exchange
Green Impact Exchange has named John Visneski as Chief Information Security Officer, where he will lead enterprise technology and cybersecurity strategy, overseeing secure operations and regulatory compliance as the exchange builds out its platform. He joins from Sumo Logic, where he served as CISO, and previously held the same role at MGM Studios, later taking on a security leadership position at Amazon focused on mergers and acquisitions.
Joe Giannetti – Chief Information Officer and Chief Information Security Officer at Lexitas
Lexitas has added Joe Giannetti as Chief Information Officer and Chief Information Security Officer, giving him responsibility for the company’s technology operations, infrastructure, business systems, and cybersecurity programs. He will help scale internal platforms and support continued innovation across the litigation support services provider. Giannetti joins from Employ, where he led IT and security and oversaw the integration of four operating companies into a unified enterprise platform, following an earlier technology leadership role at Applied Systems.
Paul Adams – Chief Information Security Officer at Blue Mountain
Paul Adams has been appointed Chief Information Security Officer at Blue Mountain, where he will lead the company’s enterprise security, compliance, and AI governance initiatives. Adams brings more than 25 years of experience in SaaS and enterprise technology and previously spent more than a decade at CrunchTime, leading infrastructure, information security, and governance, risk, and compliance programs. At Blue Mountain, he will help advance the company’s security architecture and ISO 27001, SOC 2, and ISO 42001 compliance efforts.
Jerry Hoff – Chief Information Security Officer at Myota
Myota has named Jerry Hoff as Chief Information Security Officer, where he will lead the company’s security strategy and help advance adoption of its data-centric cyberstorage platform. Hoff brings more than 20 years of enterprise and application security experience spanning financial services, manufacturing, and large-scale enterprise environments. He previously founded a static application security testing company acquired by WhiteHat Security and later held senior security leadership roles at Sony Electronics and NTT, including serving as Global Head of Security at Sony.
Jacob Berry – Chief Information Security Officer at Fable Security
Jacob Berry has been appointed Chief Information Security Officer at Fable Security, bringing 18 years of experience in cybersecurity, incident response, cyber operations, governance, compliance, and security leadership. In his new role, Berry will help guide the company’s security strategy while supporting customers in addressing human-centric cybersecurity risks. He joins Fable Security as the company continues to expand its secure behavior management platform for enterprise customers.
Victor Chang – Chief Information Security Officer at Backstory
Victor Chang has joined Backstory as Chief Information Security Officer, where he will lead the company’s cybersecurity strategy, infrastructure security, and compliance programs as the AI answers platform expands its enterprise footprint. Chang brings more than 20 years of experience in cybersecurity and infrastructure leadership, most recently serving as a senior security leader at Meta, where he oversaw security and technical integrations for the company’s global mergers and acquisitions activity. His background also includes leadership roles at Amdocs and several high-growth technology companies.
Frank DePaola – Vice President and Chief Information Security Officer at Sonoco
Sonoco has brought on Frank DePaola as Vice President and Chief Information Security Officer, where he leads the company’s global cybersecurity program. DePaola joins after more than eight years at Enpro, where he served as the company’s first CISO before expanding his responsibilities to include global infrastructure, IT operations, and privacy. Earlier in his career, he held security leadership roles at General Electric, Humana, and an Applebee’s franchise group. A U.S. Army veteran, DePaola is also a graduate of Carnegie Mellon University’s CISO executive program and the FBI CISO Academy.
Suyesh Karki – Chief Information Security Officer at Aledade
Suyesh Karki has joined Aledade as Chief Information Security Officer, where he will lead the company’s Security and IT organization and oversee cybersecurity efforts supporting its expanding use of AI and data analytics. Karki brings more than 20 years of experience, most recently serving as CISO and Vice President of Information Security at BambooHR. Previously, he held the CISO role at Domo, where he led cloud security and compliance initiatives, including the company’s HITRUST certification. Earlier in his career, he advised healthcare and enterprise clients on data protection at Ernst & Young. At Aledade, he will help safeguard health information for more than 3 million patients across its network.
CxOs on the Move is brought to you by the Celigo. Celigo makes your systems work together and your AI work for you, with one platform to connect, automate, and govern.