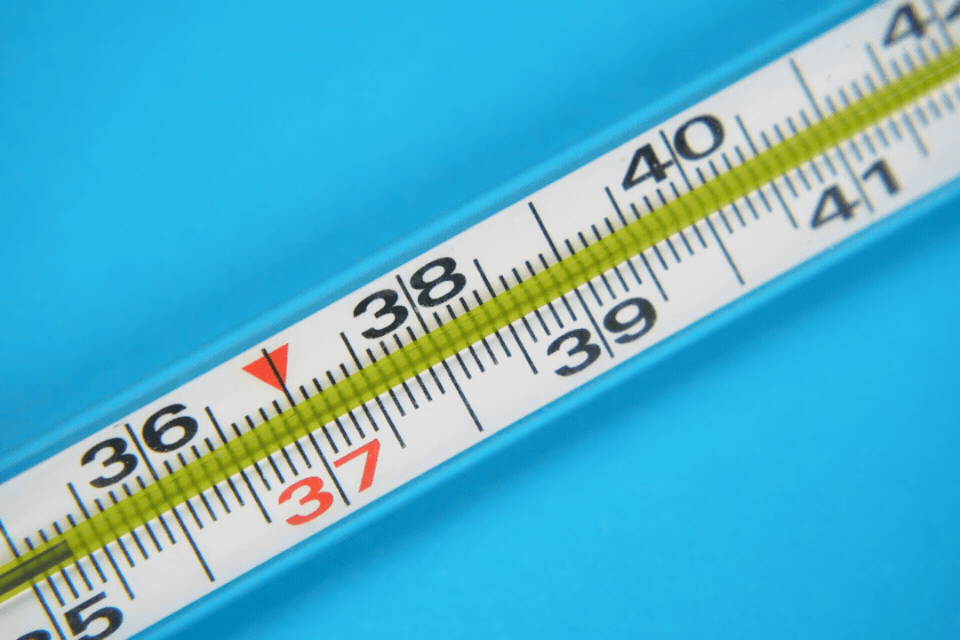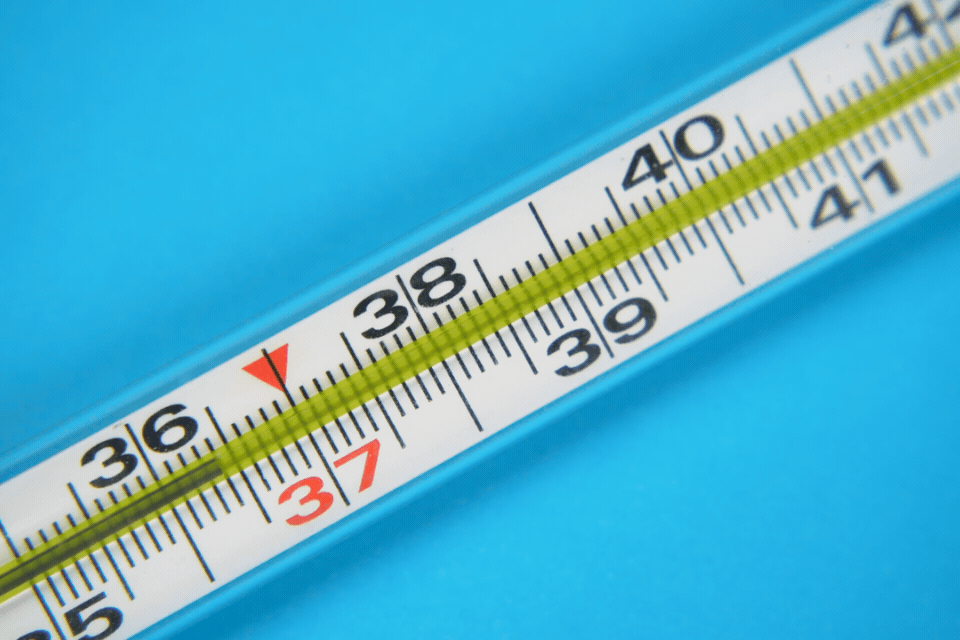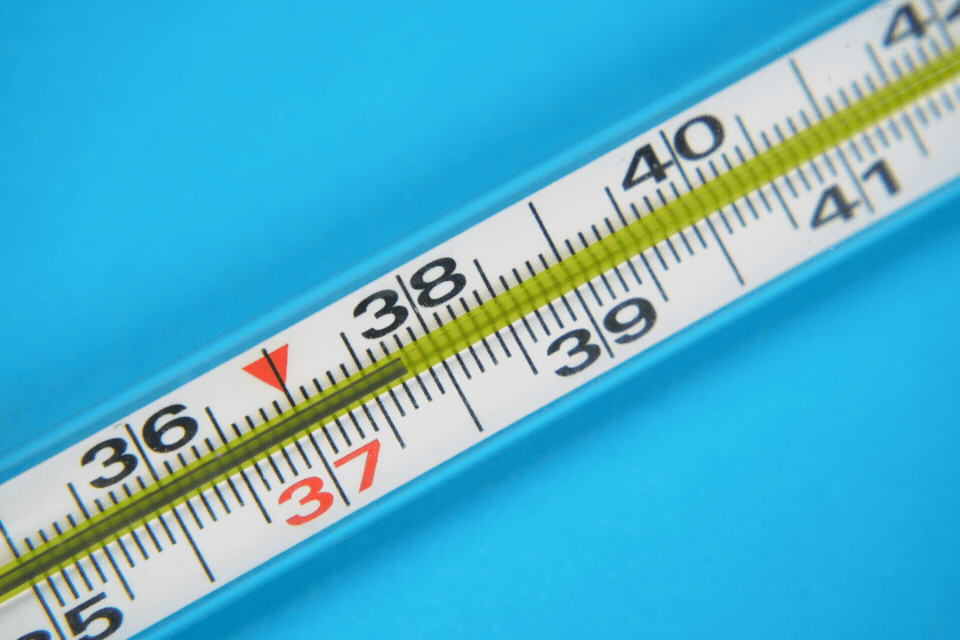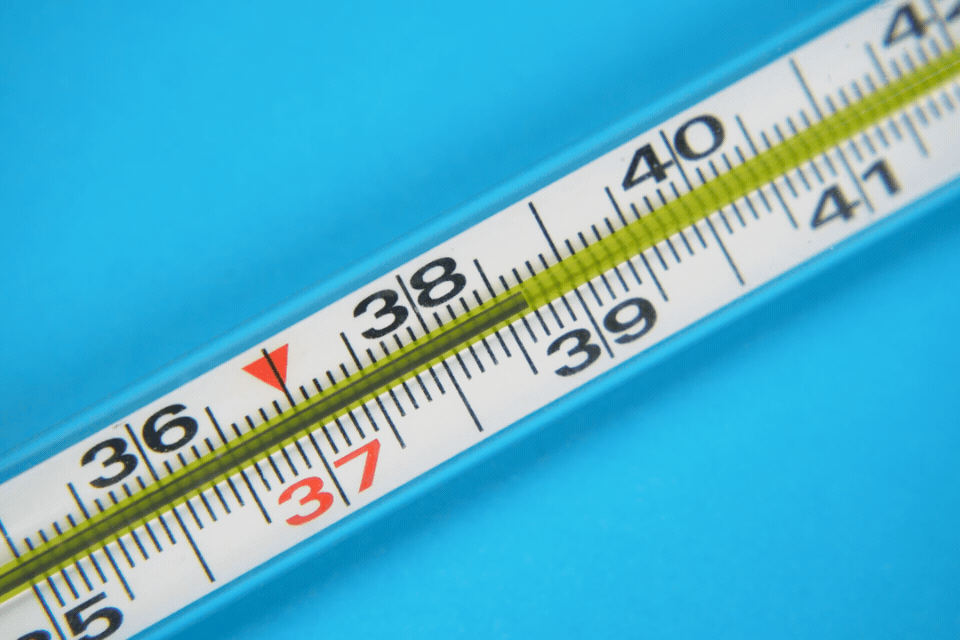
Hundreds of supermarkets across France were affected by a cyberattack that allowed hackers to remotely change refrigeration settings, sending temperatures in some units as high as 50°C (122°F).
The attack began overnight on October 11 and disrupted several of France’s largest supermarket chains. Some stores were forced to discard spoiled food, with financial losses potentially reaching tens of millions of euros.
At the center of the incident were refrigeration controllers manufactured by Danish company Danfoss, including older models that no longer receive security updates. French authorities have issued a cybersecurity alert and opened an investigation into how the attackers gained access.
Why It Matters: Aging equipment can be difficult to secure, especially when it falls outside traditional IT oversight or depends on third-party providers for maintenance. The financial losses facing French retailers show how vulnerabilities in these systems can affect daily operations. For organizations that rely on connected equipment, understanding who has access and where security responsibilities lie is an important part of managing business risk.
- Disruptions Reached Hundreds of Locations: At least 300 stores belonging to one of France’s largest supermarket groups were affected, with several other major grocery chains reporting dozens of incidents. The extent of the damage depended on how quickly stores responded. Some maintained safe temperatures with help from staff and maintenance contractors, while others had to discard spoiled inventory. Industry estimates suggest losses across France could reach tens of millions of euros.
- Attackers Used Existing Controls to Interrupt Cooling: Refrigeration controllers manage equipment across stores, including freezers, chilled displays and compressors. Hackers reportedly manipulated the built-in defrost function, preventing equipment from maintaining safe temperatures. Some units reached 50°C, and authorities received reports of equipment beginning to catch fire. With multiple refrigeration units connected to centralized controls, attackers could cause significant disruption without accessing each piece of equipment individually.
- Unsupported Controllers Complicated Security Options: Among the affected devices were Danfoss AK-SM 800 and AK-SC 355 controllers, which reached end-of-life status in 2021 and 2016. Neither receives security updates, and some newer AK-SM 800A controllers running outdated firmware were also affected. Replacing refrigeration control systems can require specialized labor and interruptions to store operations, making upgrades more difficult than routine IT hardware replacements.
- Researchers Previously Identified Security Vulnerabilities: Security researchers had identified thousands of internet-accessible Danfoss AK-SM 800A management interfaces, along with vulnerabilities that could allow attackers to bypass authentication or execute remote commands. Fixes were released in 2025, although investigators have not established whether those flaws played a role in the attack. Following the incident, French cybersecurity authorities advised organizations to disconnect affected controllers from the internet or restrict access while the investigation continues.
- Third-Party Maintenance Complicates Security Oversight: Many supermarkets rely on outside contractors to maintain and remotely monitor refrigeration equipment. Some affected retailers confirmed that their systems were supplied through third-party providers, creating additional considerations around who manages access and security updates. French cybersecurity authorities have recommended restricting remote connections, reviewing user accounts and changing credentials. These arrangements can make it harder to establish clear responsibility for securing equipment that remains connected to business operations.
Go Deeper -> Attackers Reportedly Hack Supermarket Fridges and Raise Temperatures to 50°C – CSN